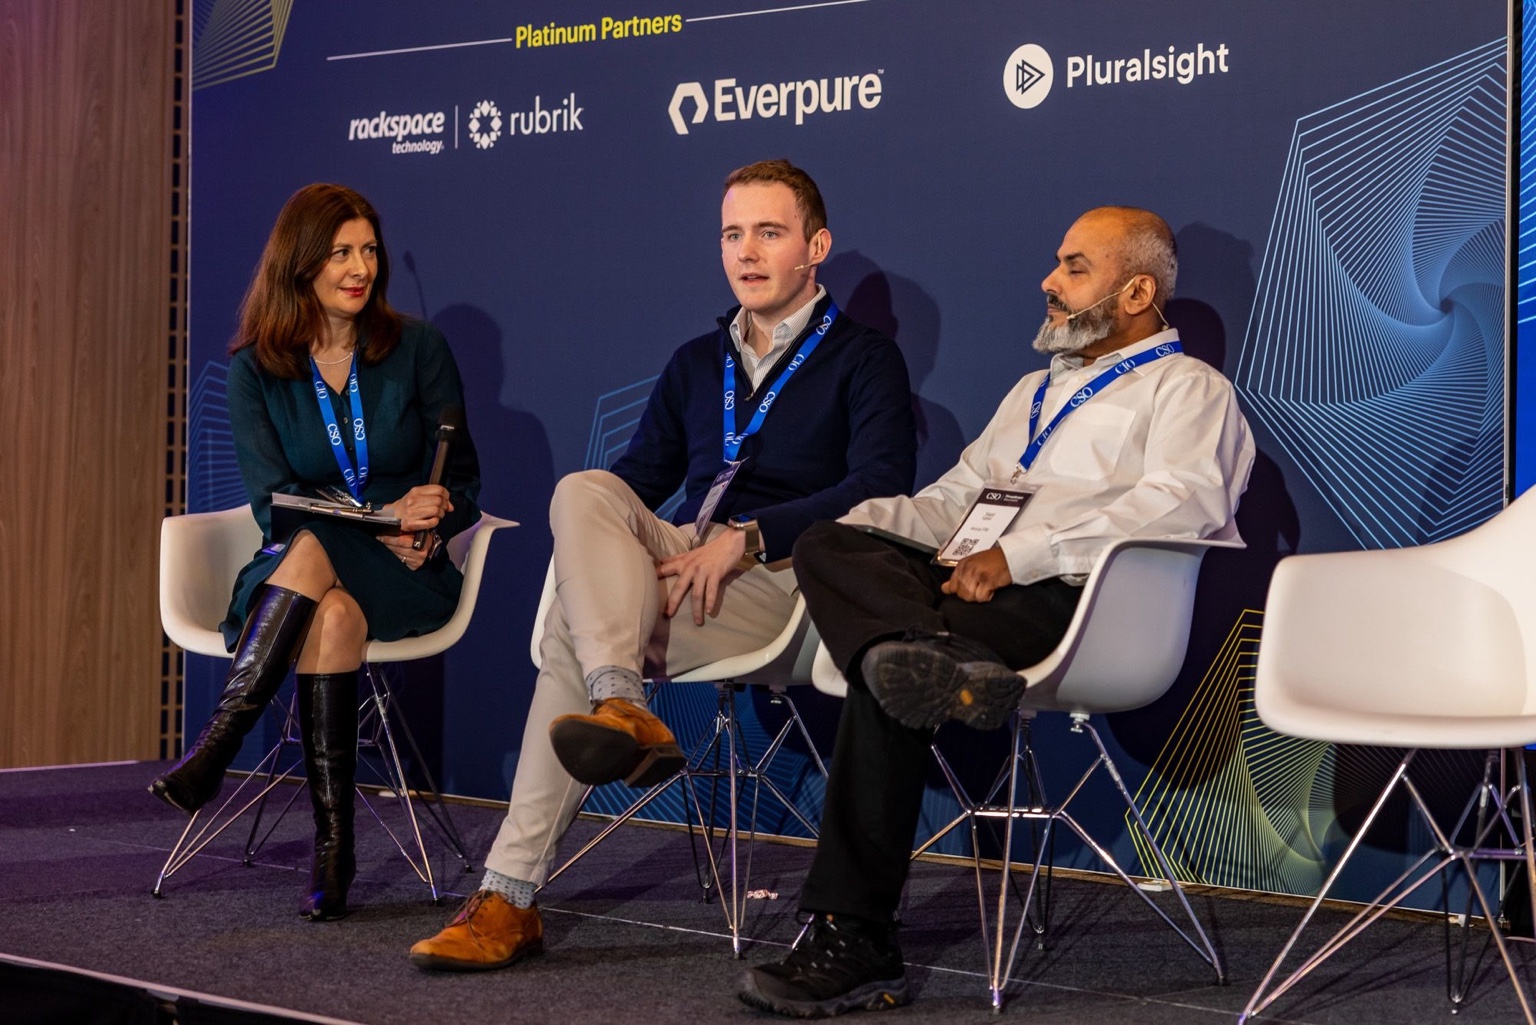
CSO / SECURITY LEADERSHIP
Security by design
At CSO ThreatScape Manchester, I discussed how leaders can build security into AI, cloud and connected systems. I explore the same challenge in my CSO Online article, “Innovation without exposure”.
IT & CYBER SECURITY CONSULTANCY FOR SMEs

30 minutes to explore how I can build, hack or defend your systems.
Work directly with Luke Collinson on bespoke software, automation and practical cyber security. Start with a conversation, a clear scope and an agreed outcome.
Organisations connected to Luke’s education, career and professional recognition.
BUILD A BETTER WAY TO WORK
I design and build bespoke business platforms, automation and analytical tools around how your organisation works, from connected everyday operations to complex mathematical modelling. I build web applications with HTML, CSS, JavaScript and PHP. I also program in Python, C#, C++ and C, and use MATLAB for numerical modelling.
From custom business platforms to algorithms for risk analysis and actuarial work, the solution starts with your needs, data and intended outcomes.
IMPROVE THE FOUNDATIONS
Understand where your systems are exposed, prioritise the improvements that matter, and get help putting them in place.
Start with a review, agree the priorities, then improve the controls that matter most to your business.
PENETRATION TESTING
Scoped penetration testing to identify security weaknesses in your systems, understand their impact and prioritise practical fixes.
I was trained by the National Cyber Security Centre (NCSC).
Understand where you are exposed and give your team clear, actionable next steps.
GOVERNANCE, RISK & COMPLIANCE
Flexible, ongoing cyber governance, risk and compliance support for your business. Work with Luke to prepare for GDPR obligations and ISO/IEC 27001, with practical priorities and clear evidence of progress.
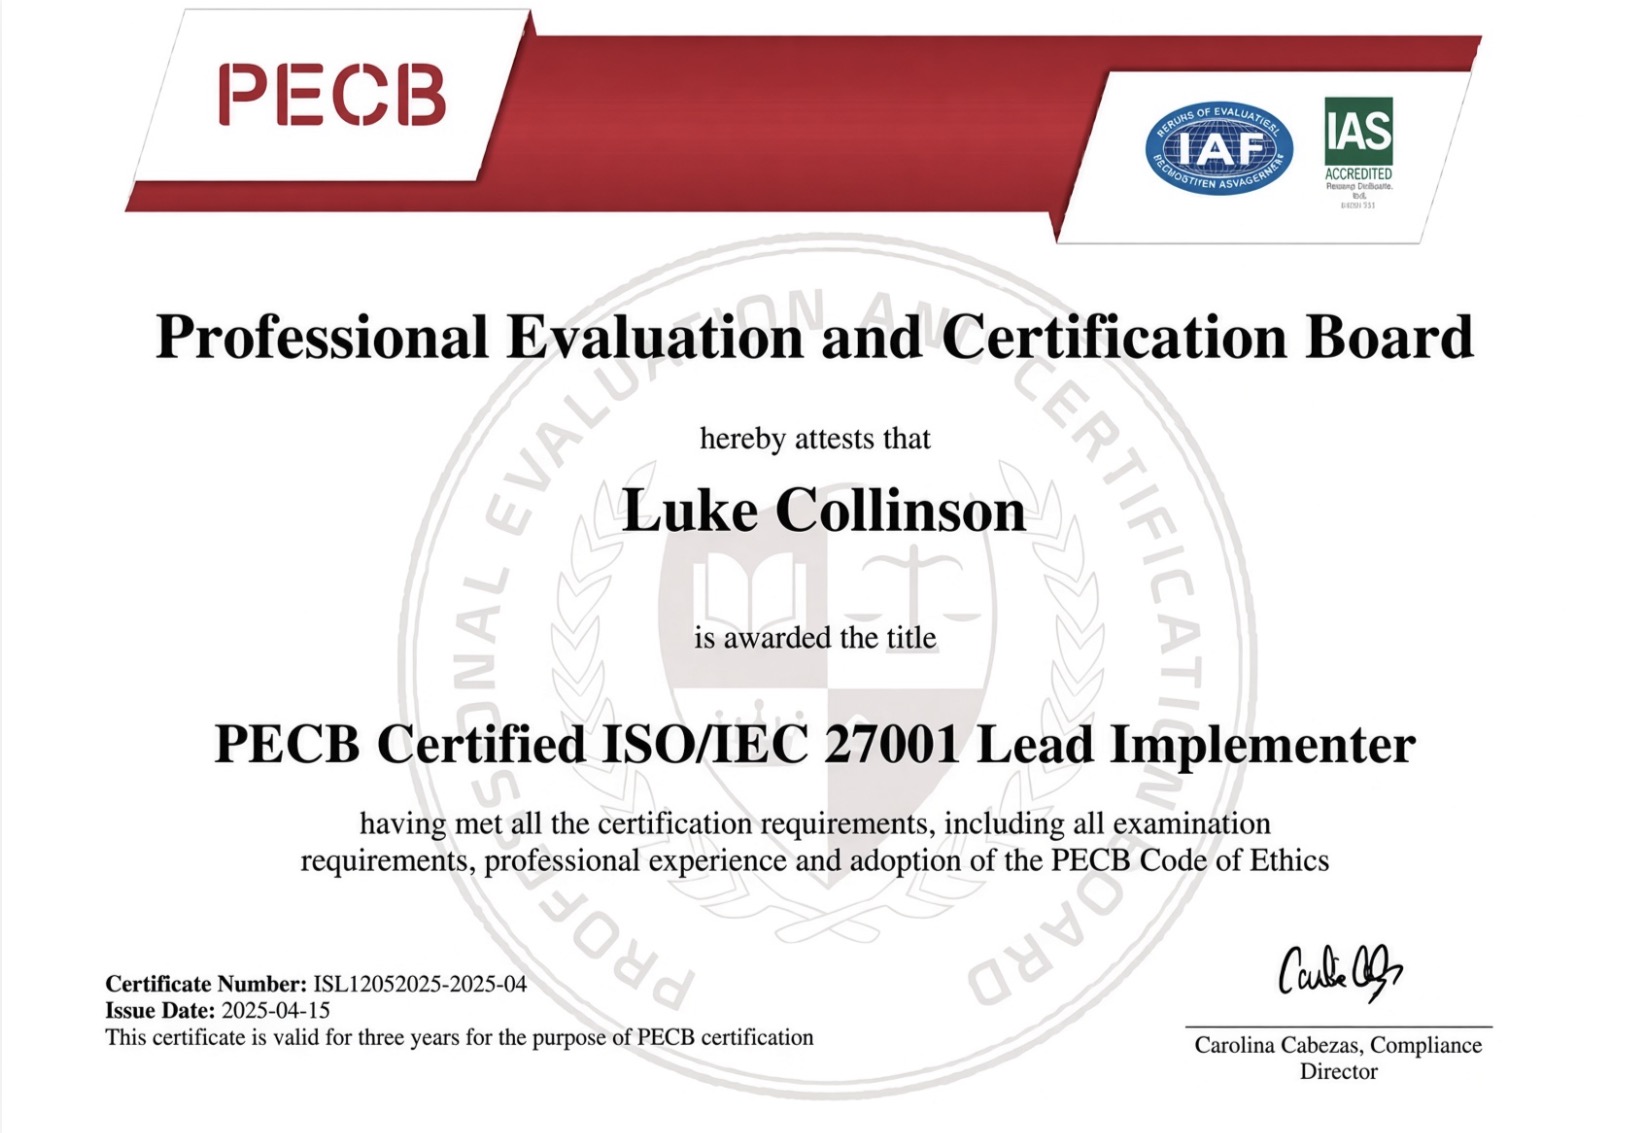
Support shaped around your organisation, its risks and the requirements you need to prepare for.
HELP WHEN AN INCIDENT HAPPENS
If your business is facing an active or suspected cyber incident, contact me directly for help. I can work with your team to understand what has happened, coordinate the response and support recovery.
Planning ahead? Book a conversation about incident readiness and response planning.
CLOUD ARCHITECTURE
I’m a qualified Microsoft cloud architect and AWS solutions architect. I can design and build the resources you need in Microsoft Azure or Amazon Web Services, whether you’re launching an application or moving an existing system to the cloud.
CSO30 UK AWARDS / 2024
I ranked 16th among UK CISOs in the 2024 CSO30 awards. The CSO30 award recognised my work building incident response capability, so teams could act with confidence when an incident happened.
I also won the Business Enablement Award for negotiating security contracts with Immersive Labs and RoboShadow at Salford City Council. Both experiences shape how I advise clients on what to buy and how to respond when something goes wrong.
Read my Foundry profile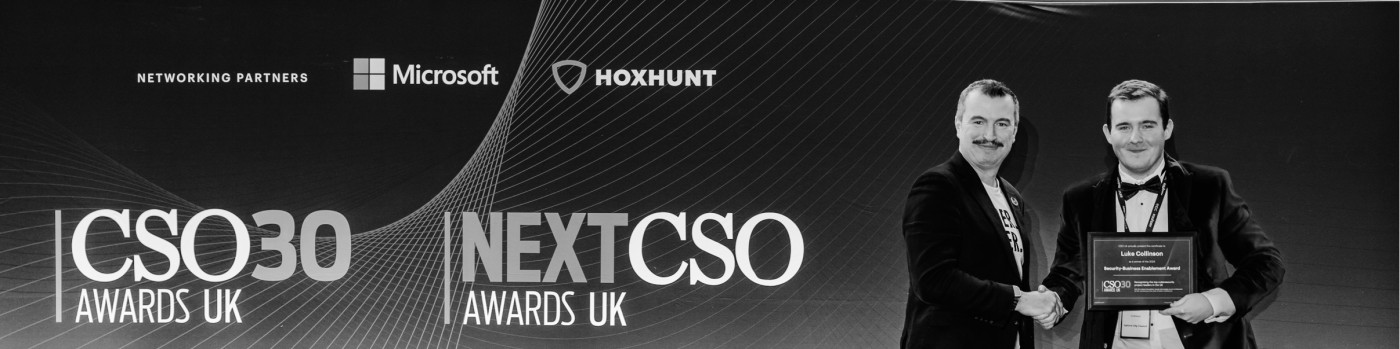
ENGINEERING IN ENTERPRISE
The Royal Academy of Engineering selected me for its Enterprise Fellowship, supported by the ERA Foundation. Admission to the programme is highly selective. The Academy’s Enterprise Hub is ranked the UK’s leading startup hub and one of Europe’s best by the Financial Times, Statista and Sifted.
Fellows receive training in finance, negotiation and leadership, alongside mentoring as they bring engineering ideas to market. I apply that training when helping a business decide whether a technical idea is worth building, what it will cost and who will use it.
ON STAGE AND IN PRINT
I speak about innovation and security leadership with the people who build technology and the leaders who decide how to use it. My talks draw on decisions I have faced myself, from investigating incidents to introducing new technology safely.
CSO / SECURITY LEADERSHIP
At CSO ThreatScape Manchester, I discussed how leaders can build security into AI, cloud and connected systems. I explore the same challenge in my CSO Online article, “Innovation without exposure”.
TECHUK / INNOVATION
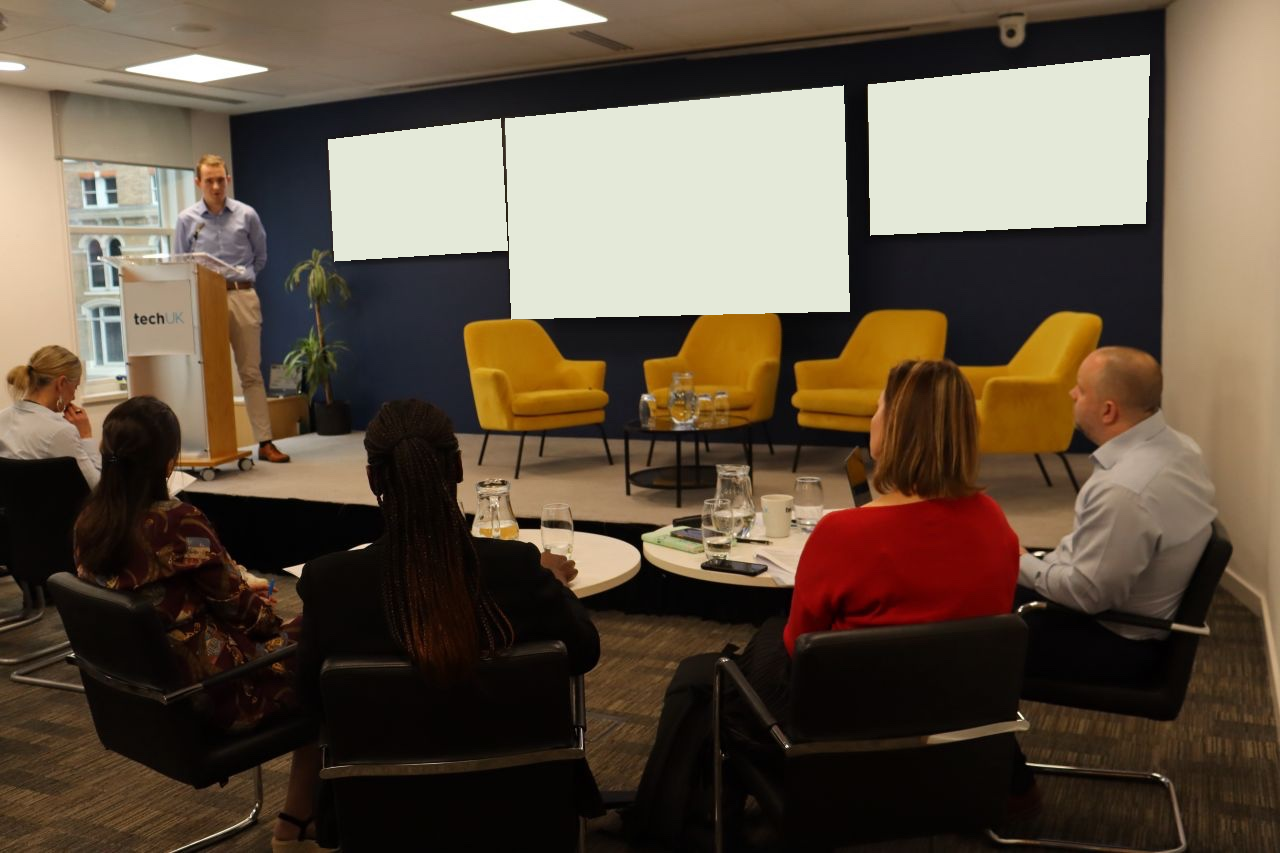
At techUK’s Cyber Innovation Den, I presented my earlier cyber resilience work to industry judges. It was one of ten pitches in 2025 and received a commendation from the panel.
View the techUK post
LONDON BLOCKCHAIN CONFERENCE
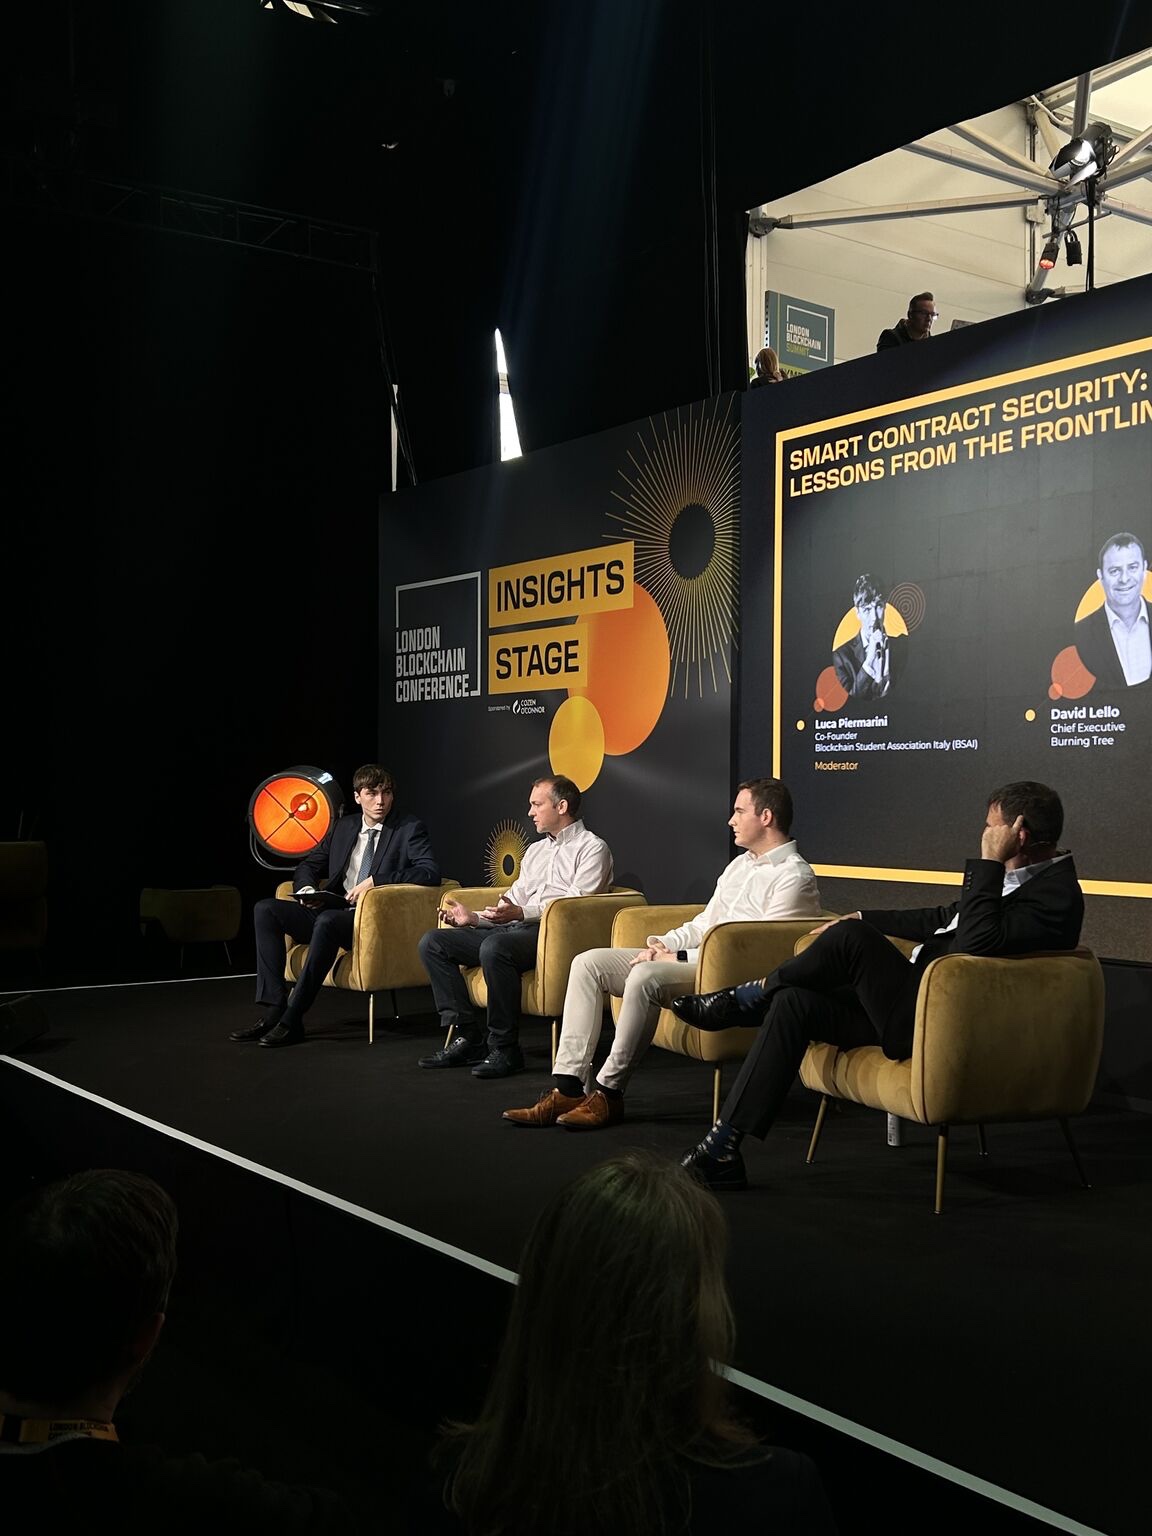
I joined the Insights Stage in London for a discussion on smart contract security, bringing the perspective of an incident responder to the risks facing teams deploying new systems.
View the conference speakersHOW WE WORK TOGETHER
Tell me what is getting in the way, how your team works and what you want to improve.
We agree the priorities, deliverables, timing and cost before work begins.
Get a focused review, a scoped implementation project or ongoing advice, with a clear handover and next steps.
03 / YOUR CONSULTANT
Cyber security, governance and risk.
Practical engineering experience.
I combine experience leading cyber security with building custom platforms, automation, algorithms and mathematical models. My approach connects technical decisions to the needs of the people running the business.
I was trained by the National Cyber Security Centre (NCSC).
My professional experience includes Head of Cyber Security at JLA Group, Cyber Security Engineer at AstraZeneca, Cyber Defence Analyst at Aldermore Bank and Threat Hunter at Rolls Royce.
Previous work includes Python security tooling, automated threat intelligence integration and an internal file forensics platform. This experience informs how I approach bespoke business solutions.
EXPERIENCE / 2019 TO TODAY
Each step has shaped how I work: investigate carefully, build practical solutions and connect technical decisions to what the business needs. Explore the story below.
Learning to solve complex problems
My Mechanical and Nuclear Engineering studies gave me a foundation in analysing complex systems and testing assumptions. Winning the TARGETjobs Construction and Engineering Undergraduate of the Year award led to a placement with Laing O’Rourke at Manchester Airport.
Working across engineering disciplines showed me that a useful solution has to fit the people, processes and practical constraints around it. That is still where I start with a consulting brief.
Turning evidence into clear decisions
At the Home Office, I analysed datasets containing more than 100,000 records and produced impact assessments, policy and process documentation to support legislative change.
The experience taught me to turn complex evidence into clear recommendations, and to think carefully about how a decision affects the people who have to put it into practice.
Understanding how attacks unfold
Following the CyberFirst programme, I moved into proactive threat hunting at Rolls Royce. I investigated signs of compromise, developed investigative tools and worked with security operations and intelligence teams.
That investigative grounding helps me look beyond a checklist: understand what an attacker could do, identify the evidence and explain which weaknesses deserve attention first.
Making security tools work together
At Aldermore, I helped migrate security monitoring to Microsoft Sentinel, integrated threat intelligence and developed detection content for financial services threats.
This developed my approach to integrations: connect the right information, reduce gaps between tools and make the result useful to the team relying on it.
Building tools that remove manual work
At AstraZeneca, I built Python tooling, integrations and an internal file forensics platform to improve investigation and response workflows. I also led shifts of five people as the person on point.
Building for colleagues doing the work reinforced a practical lesson: automation should remove repetitive effort, make information easier to use and support human judgement.
Taking responsibility for business resilience
As Head of Cyber Security, reporting to the CTO, I built an information security management system from scratch and implemented technical controls across the organisation. My remit included incident response, supplier relationships, procurement and advising senior stakeholders.
I helped automate Azure recovery using ARM and Bicep, and a change of security operations provider saved £75,000. In 2024, I received a CSO30 UK award, ranked 16th among UK CISOs. This is the experience I bring to consulting: connect sound engineering to recovery, proportionate investment and decisions the business can act on.
Oxford graduate studies in Software and System Security
Oxford graduate studies in Software and System Security build on my experience of security operations, engineering and leadership.
I bring that combination to consulting by questioning assumptions, looking at the wider system and explaining the tradeoffs behind a recommendation.
Taking an idea into industry
My earlier cyber resilience work was highly commended at techUK’s Cyber Innovation Den 2025, where ten innovators pitched their ideas to an industry panel.
Presenting a technical idea to that audience sharpened how I explain the problem, the value of the proposed solution and what still needs to be proved. Those questions matter just as much when scoping a client project.
Turning engineering into a business
As an ERA Foundation Enterprise Fellow with the Royal Academy of Engineering, I am developing the commercial judgement that turns an engineering idea into something customers can use and value.
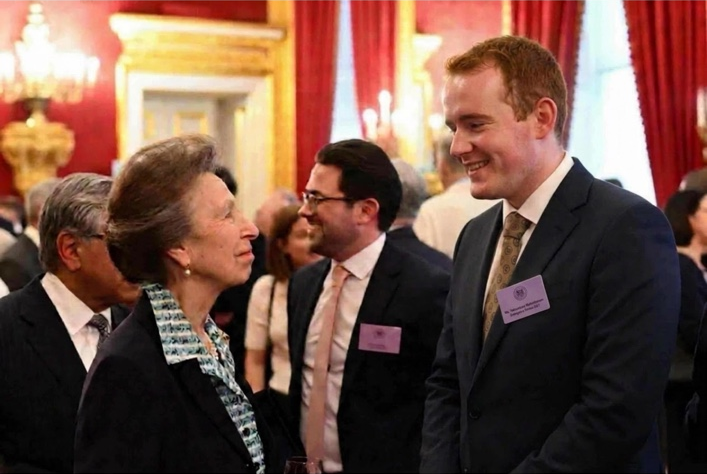
The fellowship brings customer discovery, mentoring and business development alongside technical work. My wider Academy connections began with an Engineering Leaders Scholarship and have included the opportunity to meet HRH The Princess Royal.
Listening to the wider industry
Joining the UK cyber security trade mission to RSA Conference in San Francisco gave me the opportunity to discuss security challenges with an international audience of technology and business leaders.
Those conversations reinforce how I approach consultancy: listen to the operational problem first, test whether a proposed solution is useful and make its value clear.
Contributing to security leadership and business
I contribute to security leadership and business through industry speaking, panel discussions and writing. From CSO events to the London Blockchain Conference, I share practical perspectives on security, emerging technology and the decisions facing business leaders.
My CSO Online article, “Innovation without exposure”, explores how security leaders can enable innovation while improving resilience and reducing repetitive work. It reflects my consulting approach: make security useful to the business and measure the outcome.
Bringing that experience to your business
Building CSS Labs and now CordonGrid has brought together engineering, cyber security and the day to day realities of running a business: understanding customers, choosing priorities and making limited resources count.
I now work directly with businesses on custom software, automation, cyber security and incident response. We start with the problem, agree what a useful result looks like and shape the work around your team.
From hands on controls to supplier decisions and recovery planning, I connect security priorities to the way your business operates.
Custom software and automation informed by experience building tools for the people who use them every day.
Complex evidence turned into understandable options, an agreed scope and practical next steps.
LET’S TALK ABOUT YOUR BUSINESS
Tell me what your business does, what is getting in the way and what a useful result would look like. We can discuss the right next step and agree a scope before work begins.